 Getting Started

 Trainings
 News
 FAQs
 Webinars
Simploud Permission Sets
This article describes the latest version of the Permission Sets module, available to all Simploud customers who joined from August 2026 onward.
In the past, permissions were managed primarily at the Profile level and/or through designated module permission sets. Today, we primarily use Identity Packages (Profile-based) to grant access to different modules.
If you are using a different permissions configuration, you are welcome to contact the Simploud Success Team for more information about the access configuration relevant to your environment.
The New Permission Sets Module
In the new Permission Sets module, Identity Packages are used to grant access to different objects and processes within the system.
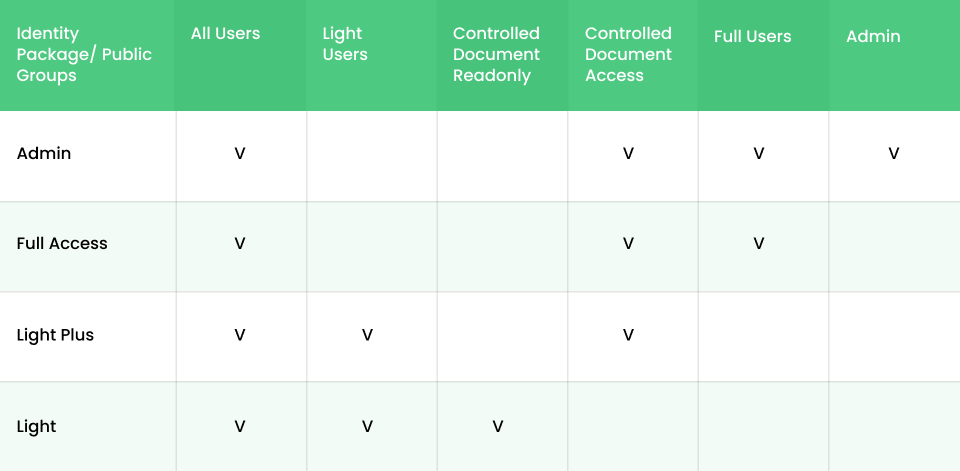
The level of access that can be assigned depends on the user’s Profile. Each Profile has its own Identity Package, which consists of Permission Sets and Public Groups.
Permissions to create, edit, or read records in different processes (objects) in the system (e.g., Controlled Documents, CAPAs, etc.) should be managed through Permission Sets. The relevant permissions are assigned to the appropriate Identity Package, after which an Admin with access to the Simploud Administration page can assign the relevant Identity Package to users, as described below.
Continue using AI Cursor?Keep it onTurn Off
The Profiles
Simploud has four user Profiles:
- Admin: Intended for users responsible for system administration and configuration. Users with this Profile have read and edit access to all relevant Simploud objects.
- Full User: Intended for users who require full access to Simploud objets without administrative access. Users with this Profile can have read and edit access to all relevant Simploud objects.
- Light Plus User: Intended for users who require read access to all Simploud objects and edit access to Controlled Documents only. They do not have edit access to other Simploud objects.
- Light User: Intended for users who require read-only access to Simploud.
All four profiles have access to perform tasks in the system (i.e Training/Read and understand)
Permission Sets for Different Identity Packages
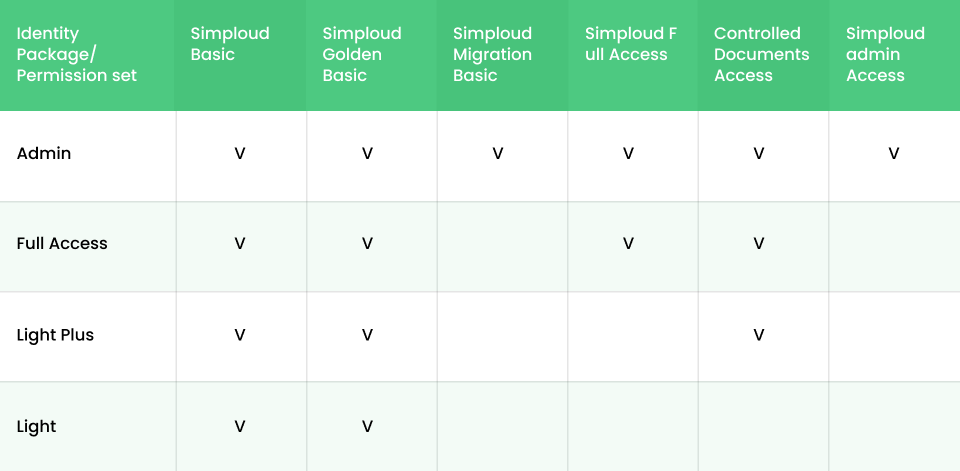
Each Profile requires the assignment of different Permission Sets, depending on the access and capabilities associated with the Profile. This is the list of standard permission sets in use:
- Simploud Basic: The default Permission Set automatically assigned to all users upon user creation. It provides access to use the Simploud code package.
- Simploud Golden Basic: Provides additional basic functionalities relevant to all users, such as performing tasks and granting viewing access to all the objects in your scope.
- Simploud Migration Basic: Relevant only for QA environments. Provides the permissions required to work with Configuration Items.
- Simploud Full Access Permission: Grants edit access to Simploud objects in scope, except Controlled Documents.
- Controlled Documents Access: Grants read and edit access to Controlled Documents.
- Admin: Provides access to Simploud Administration, Validation and Configuration Items.